


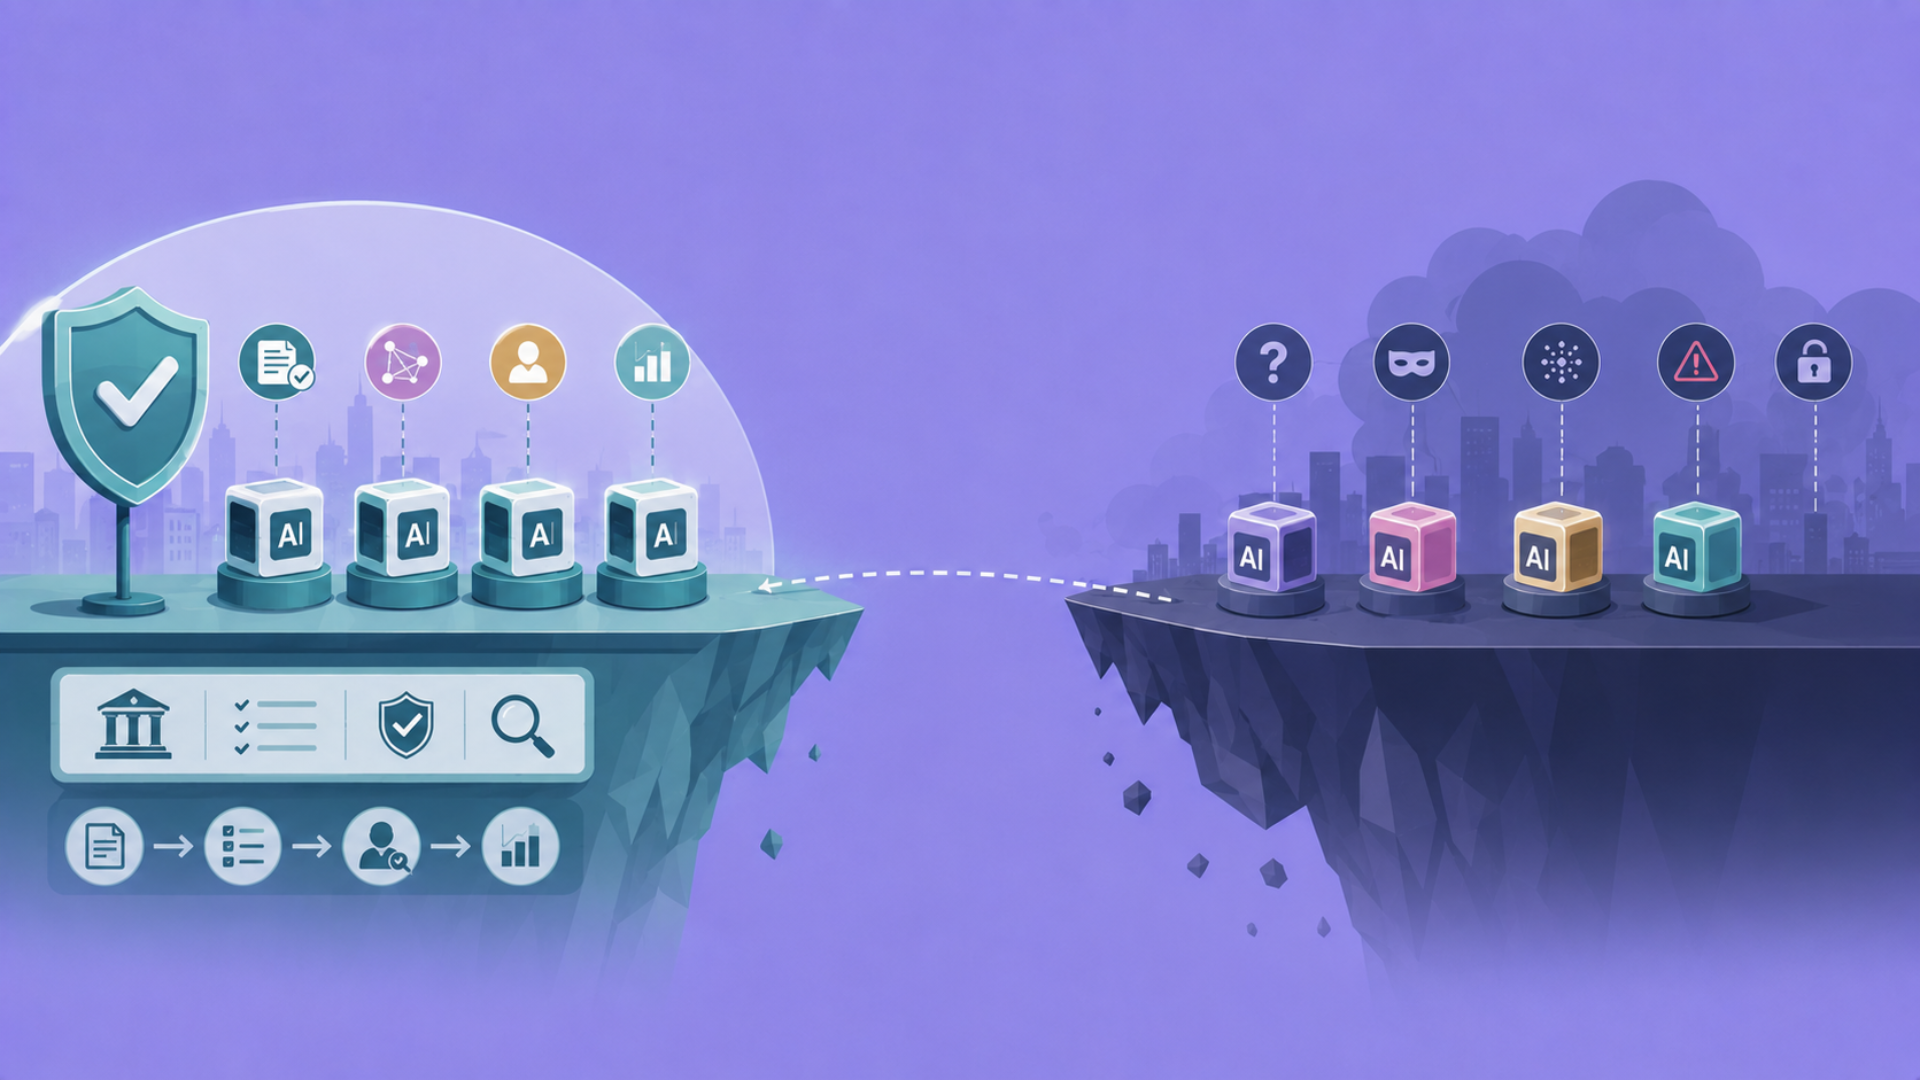
Only 8% of organisations that use AI maintain a comprehensive governance framework. That figure comes from Deloitte's State of AI in the Enterprise 2026 report, based on 3,235 respondents from director to C-suite level across 24 countries.
The other 92% are running AI with partial or no formal governance coverage.
This is not a problem confined to smaller organisations with limited resources. The governance gap exists at enterprise scale, across regulated industries, and in organisations that have published responsible AI policies and appointed AI ethics teams. The gap is between what is documented and what is enforced.
It is showing up in audit findings. It is showing up in security incidents. And with the EU AI Act's full enforcement provisions now in effect for high-risk systems, it is beginning to show up in regulatory exposure.
What the Gap Actually Looks Like
The governance gap is not simply that enterprises lack policies. Most have them. The gap is between policy and enforcement.
A Cloud Security Alliance study found that 63% of enterprises cannot enforce purpose limitations on their AI agents. The policy says the agent should only access data relevant to its task. The controls to enforce that limitation in practice do not exist or are not monitored.
60% cannot terminate a misbehaving agent once it is running. The policy says agents will be shut down if they operate outside their defined parameters. The capability to detect misbehaviour and act on it in real time is not in place.
74% of organisations give AI agents more privileges than each specific task requires. The policy of minimum necessary access is documented. It is not applied in the system architecture.
By April 2026, 65% of enterprises with deployed AI agents had experienced a confirmed security incident. Stanford's 2026 AI Index found that security and risk is now the primary barrier to scaling agentic AI, cited by 62% of organisations. It outranked technical limitations and regulatory uncertainty by 24 percentage points.
The bottleneck to enterprise AI scale is not model capability. It is governance.
Why the Gap Persists Despite Significant Investment
Most enterprises are spending on AI governance. The Gartner AI governance platform market is projected to reach $492 million in 2026. ServiceNow, Microsoft, and Google all made governance central to their major 2026 announcements. Organisations deploying dedicated AI governance platforms are 3.4 times more likely to achieve high effectiveness in their governance programmes than those that do not.
Yet the gap persists. The reason is structural rather than budgetary.
In a typical large enterprise, AI governance is fragmented across functions. The CISO owns AI security risk. The legal team controls contracting language. The compliance team defines regulatory requirements. HR writes acceptable use policies. Each function owns a slice. None of them owns the outcome.
Each team builds its own rules. Business units often duplicate governance efforts across enterprise-wide AI initiatives. Policies are written but not enforced. Risk assessments happen in silos. Decisions stall because no single authority can approve or block an AI deployment.
The result is predictable. AI deployment continues regardless. Demand for AI does not wait for governance to catch up. The enterprise ends up with a growing population of AI systems operating outside the governance framework simply because the framework could not keep pace with deployment.
Deloitte found that 84% of companies have not redesigned roles around AI. Only 21% have a mature AI agent governance model. Yet approximately 75% plan to deploy agentic AI within two years. The gap between deployment velocity and governance maturity is not closing. It is widening.
What Good AI Governance Actually Requires
The organisations that are closing the governance gap share a common characteristic. They have built governance into the AI architecture rather than documenting it in policy.
This distinction matters more than any specific framework or platform choice. A governance policy that exists in a document but is not reflected in how the AI system is built will not prevent the failures it is designed to prevent. A governance framework that is embedded in the access controls, audit trails, and operating parameters of the AI system will.
Four elements distinguish governance that is built in from governance that is bolted on.
Access controls that enforce minimum necessary privilege:
The AI agent or system should only be able to access the data and systems that each specific task requires. This is not a policy decision. It is an architectural decision made when the system is built. Retrofitting least-privilege access onto systems that were deployed with broad permissions requires significant rework. Building it in from the start does not.
Audit trails that are generated automatically:
Every action taken by an AI agent should produce a record. What data was accessed, what decision was made, what action was taken, and when. This record should be generated by the system without requiring manual documentation. In regulated industries, this audit capability is not optional. The EU AI Act requires it for high-risk AI systems. Forward deployed engineering in regulated industries builds this from day one rather than adding it before a compliance review.
Human oversight thresholds that are defined and enforced:
Every AI agent needs a defined boundary. Below that boundary, it acts autonomously. Above it, it escalates to a human. This boundary needs to be defined before deployment and enforced by the system architecture, not managed by the agent's own judgment about when escalation is appropriate.
Monitoring that detects governance failures in production:
A governance framework that does not include continuous monitoring of AI system behaviour in production cannot detect when governance is failing. AI drift is one category of production failure. Governance drift, where AI systems gradually operate further from their defined parameters as the environment changes, is another. Detecting it requires monitoring that is running continuously, not periodic audits.
What Regulators Are Now Requiring
The regulatory environment for AI governance has shifted materially in 2026. Voluntary frameworks are giving way to enforceable obligations.
The EU AI Act's full enforcement provisions for high-risk AI systems are now in effect. High-risk categories include AI used in credit decisions, insurance underwriting, employment decisions, and access to essential services. For enterprises in financial services, automotive, healthcare, and utilities, this is not a future compliance question. It is a current one.
The EU AI Act requires documented risk management systems, technical documentation, transparency to users, human oversight measures, and accuracy and robustness requirements for high-risk AI. Penalties for non-compliance reach 35 million euros or 7% of global annual turnover, whichever is higher.
The US regulatory landscape combines voluntary federal standards through the NIST AI Risk Management Framework with a growing state-level patchwork. California's AI legislation has established requirements that are influencing approaches in other states. The direction of travel is toward more specific, more enforceable requirements over time.
Procurement teams at large enterprises are now routinely requesting AI governance evidence from vendors and partners. Governance is becoming a commercial requirement as well as a regulatory one.
The Shadow AI Problem That Most Governance Frameworks Miss
The most critical and least addressed dimension of the enterprise AI governance gap is what happens with AI that was not provisioned by the organisation.
Employees are installing AI tools, browser extensions, and coding assistants on their own. They are using consumer AI platforms for work tasks. They are building AI workflows using personal accounts on enterprise AI services.
None of this sits inside the governance framework. The CISO was not consulted. Legal did not review the terms of service. Compliance did not assess the data handling implications. The organisation's data is flowing through systems it did not procure and cannot audit.
This is the shadow IT problem applied to AI, and it is significantly harder to manage because AI tools are far more capable than the shadow IT tools of previous decades. A spreadsheet stored in a personal Dropbox creates limited exposure. An AI system processing customer data or generating business decisions creates significant exposure.
Real-time AI access governance, which controls and audits AI usage as it happens including usage from employee-installed tools, is the layer that most enterprise governance frameworks do not yet reach. Closing this gap requires technical controls, not just policies.
Where to Start
The governance gap cannot be closed by writing more policy. It can only be closed by building governance into how AI systems are deployed and operated.
For most enterprises, the practical starting point is an AI system inventory. You cannot govern what you cannot see. Understanding which AI systems are running, what data they access, what actions they can take, and what oversight mechanisms exist for each of them is the prerequisite for building a governance framework that reflects reality rather than intention.
From the inventory, priority should go to the highest-risk deployments first. AI systems that make or influence decisions affecting customers, employees, or financial outcomes carry the most significant governance risk. Building robust access controls, audit trails, and human oversight mechanisms into these systems before addressing lower-risk deployments is the most efficient path to meaningful risk reduction.
The question of who owns AI governance needs a specific answer before any framework will work. A governance framework owned by a committee is not owned by anyone. A framework owned by a named individual with cross-functional authority is the starting condition for enforcement.
The AI governance gap is closing, slowly and unevenly. The enterprises closing it fastest are the ones that have stopped treating governance as a compliance exercise and started treating it as an operational requirement. The ones still producing governance documentation without enforcement capability are accumulating exposure that will become visible when the first significant incident or regulatory review arrives.
Vishleshan AI's forward deployed engineering (FDE) approach builds governance into every AI deployment from the start. Access controls, audit trails, human oversight thresholds, and monitoring are architectural components of the system, not additions made before a compliance review. Book a Consultation